Make Our Team
Your Team
We are a small DevSecOps team in Kochi, embedded in the engineering of fintech, crypto and AI companies. If owning real production early matters to you, ReGoBs would be a good fit.
Current openingsCurrent Openings
Every role is based in Kochi. Apply even if you match most of a role rather than all of it.
Engineering (2)
Role brief
What you would own
- Terraform and Terragrunt across multiple client accounts and environments
- CI/CD pipelines with approval gates that stop destructive changes
- Cloud security posture: IAM, key rotation, network boundaries, logging
- Disaster recovery that has actually been tested, not documented
What we look for
- Real AWS depth, and the scars to go with it
- Infrastructure as code as a habit, not a tool you have tried
- Kubernetes or ECS in production, at whatever scale
- Enough Python, Go or Bash to automate the thing rather than repeat it
Role brief
What you would own
- Observability across client estates: metrics, logs, traces, and their cost
- Alerting tuned so a page means something is genuinely wrong
- Incident response, the rotation, and the review afterwards
- Retention and evidence that satisfies an audit or a CERT-In question
What we look for
- You have been on call for something that mattered
- Prometheus, Grafana, CloudWatch, Datadog: any of them, deeply
- A view on what makes a postmortem useful rather than performative
- Comfort saying an alert should be deleted
Customer engineering (1)
Role brief
What you would own
- The first ninety days of every client engagement: their AWS accounts, their CI, their approval flow, and what breaks that nobody anticipated
- Being embedded in a client's engineering team rather than advising from outside, which is the whole ReGoBs model
- Turning what you see on site into runbooks, automation and product changes, with the engineers who will build them
- Being the person the client's platform team calls, and the person who tells us what they are not saying
What we look for
- Production AWS and Terraform, enough to work inside an account you did not build
- You have shipped something and then supported the people using it, and you liked the second part
- You can explain a plan diff to a CTO and to a junior engineer in the same meeting
- Comfortable in a client's Slack at six in the evening, and honest about what that costs
Security (1)
Role brief
What you would own
- Web, API, mobile and network penetration testing for client platforms
- Findings written so an engineer can act on them, with a remediation path
- Security testing wired into CI so regressions are caught, not rediscovered
- Security code review alongside the teams that wrote the code
What we look for
- Hands-on offensive experience: engagements, CTFs, bug bounty, or all three
- Fluency in the OWASP and SANS classes of issue and why they recur
- Writing that a developer will read rather than forward
- OSCP, OSWE or equivalent is welcome and not required
The Values
We Work By
Not a poster on a wall. Three things that decide how work gets done here, and that you will feel in your first week.
Ownership
We own the stack so founders do not have to. For you that means owning systems rather than tickets: you know why something is built the way it is, and you decide how it changes.
Rigour
SOC 2, SLSA 3, ISO 27001, PCI DSS. Compliance is a constraint on every design decision rather than a quarterly scramble, and it is how audit-ready infrastructure gets built instead of retrofitted.
Candour
We tell clients what is actually wrong with their infrastructure, and we tell candidates what is actually hard about the job. Over $3B in transaction volume rides on people saying the uncomfortable thing early.
Life @ ReGoBs
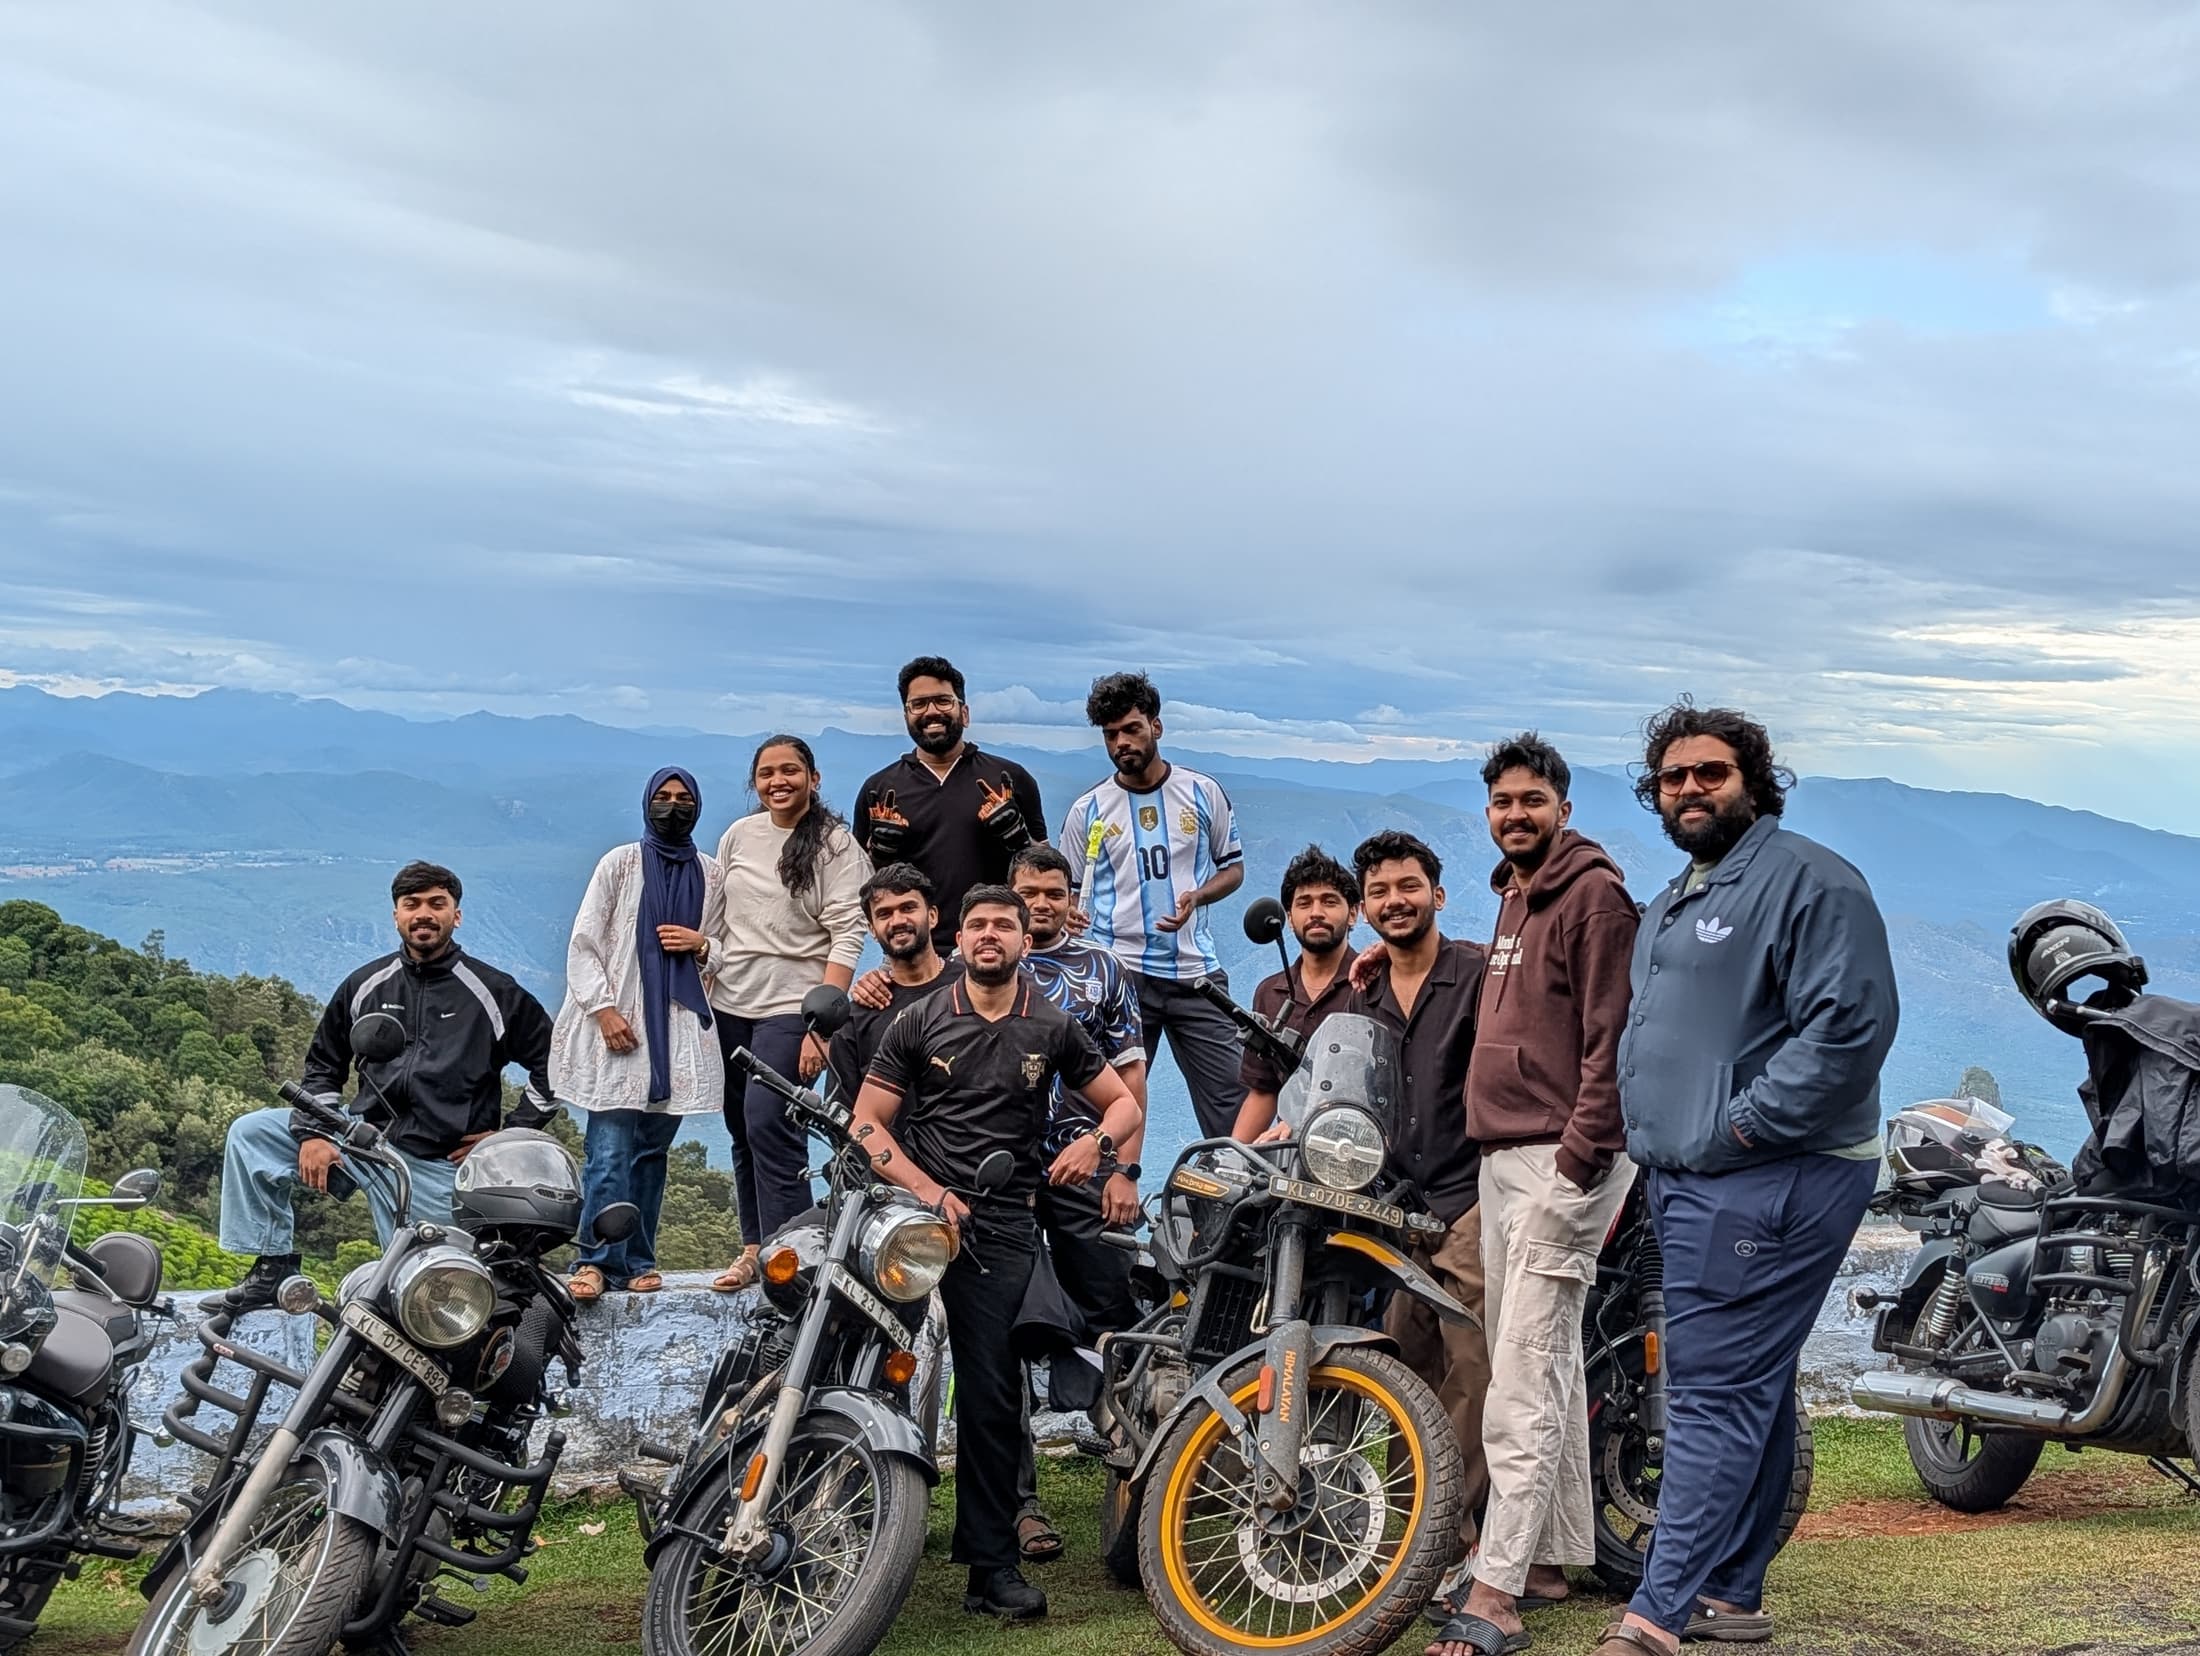
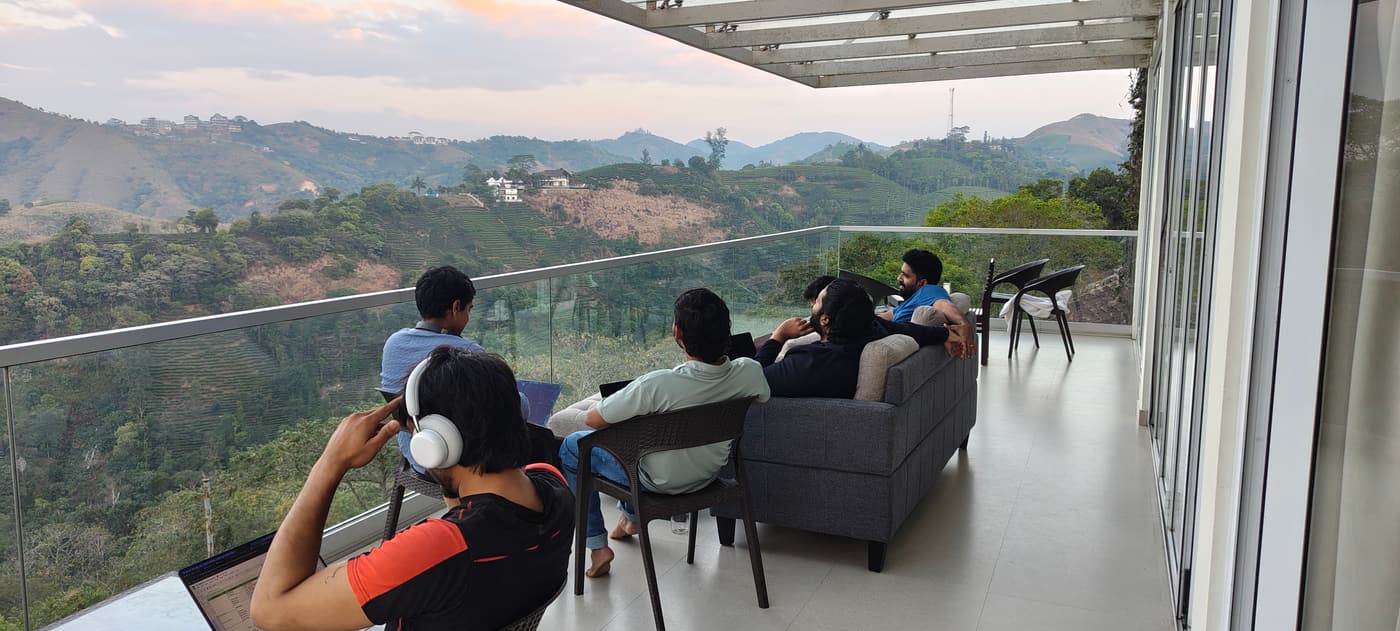
A small team in Kochi working with clients in four countries. Mostly quiet concentration, occasionally an incident call, and a lot of arguing about the right way to do something before doing it.
Why Engineers Join
Six facts about the work rather than lines from a benefits deck.
Production from month one
There is no six-month shadowing period, because there is no one to shadow. You touch real systems early, with review, and you learn faster because of it.
Seniors who have actually done it
OSWE certified, Defcon and BlackHat speakers, ex-lead at India's top-ranked CTF team. The people reviewing your work have found critical CVEs in software you use.
Audit-grade by default
SOC 2 Type II, ISO 27001, PCI DSS and SLSA 3 are the everyday standard, not a special project. That experience is rare and it travels with you.
Clients in four countries
India, the UAE, the US and the UK. Different regulators, different time zones, different expectations, and the range that comes from working across all of them.
Wide scope, not one slice
In a month you might write Terraform, tune a pipeline, read a pentest report and sit on an incident call. If you want breadth, there is nowhere better to get it.
A shared rotation, honestly described
We run production under an SLA, so there is a pager and sometimes it is yours. It is shared across the team and we say so here rather than in month three.
You Will Probably Like It Here
Nothing on this page fits but you want to work with us? Write anyway. Tell us what you have built, what you would want to own, and what you are trying to get better at. Include something real: a repository, a write-up, an incident you handled.
Write to us
Ready to apply?
A reply within five working days, either way.